
HOSTWATCH / BLOG
Evidence, explained.
Infrastructure news, practical field guides and engineering decisions from Hostwatch. Read the sources and the reasoning behind the charts and the actions.
PHP2Shell: the patch is only real when the serving process changes
A fixed image in a registry cannot repair a process that is still serving yesterday’s runtime. The October PHP advisory makes deployment identity an urgent part of the incident record.
Read the analysisMORE FROM HOSTWATCH
Architecture & practice
A CPU limit is not a percentage: reading the cgroup v2 shift
A service can become slow while the host still looks comfortable. Kubernetes’ migration guidance is a good reason to inspect the effective boundary around a workload, not just its dashboard percentage.
Read article
Unused storage belongs in a review queue, not a delete queue
A volume with no current consumer may still hold the only recovery copy of a service. Kubernetes’ new usage condition makes the first question easier; it does not answer the deletion question.
Read article
OpenTelemetry changes its security policy. Your upgrade checks need to change too.
A telemetry upgrade can preserve every public API and still change which data reaches your dashboard. OpenTelemetry’s new policy makes that distinction explicit—and gives operators a reason to test the evidence path.
Read article
Docker’s CA update exposes a familiar gap: patched tools, stale environments
A security fix can reach the image registry while an existing agent environment keeps its old trust. Docker’s October advisory is a concrete reminder to track the runtime, not just the updater.
Read article
Headlamp brings Kueue admission into view—and explains the wrong kind of Pending
A job can be waiting before there is a Pod to debug. Headlamp’s Kueue plugin makes that earlier decision visible, offering a useful lesson for every dashboard that compresses a workflow into one status.
Read article
An IP address is not a subscriber: reading client identity in Hostwatch
One customer can open thousands of connections. One public IP can carry several customers. Hostwatch needs to show both facts without treating every limit as an attack or every paired device as a subscriber.
Read article
Moving a service needs more than a destination server
The easy part is drawing an arrow between two servers. The difficult part is knowing what must move, when the destination is truly serving users and what to do if the connection disappears halfway through.
Read article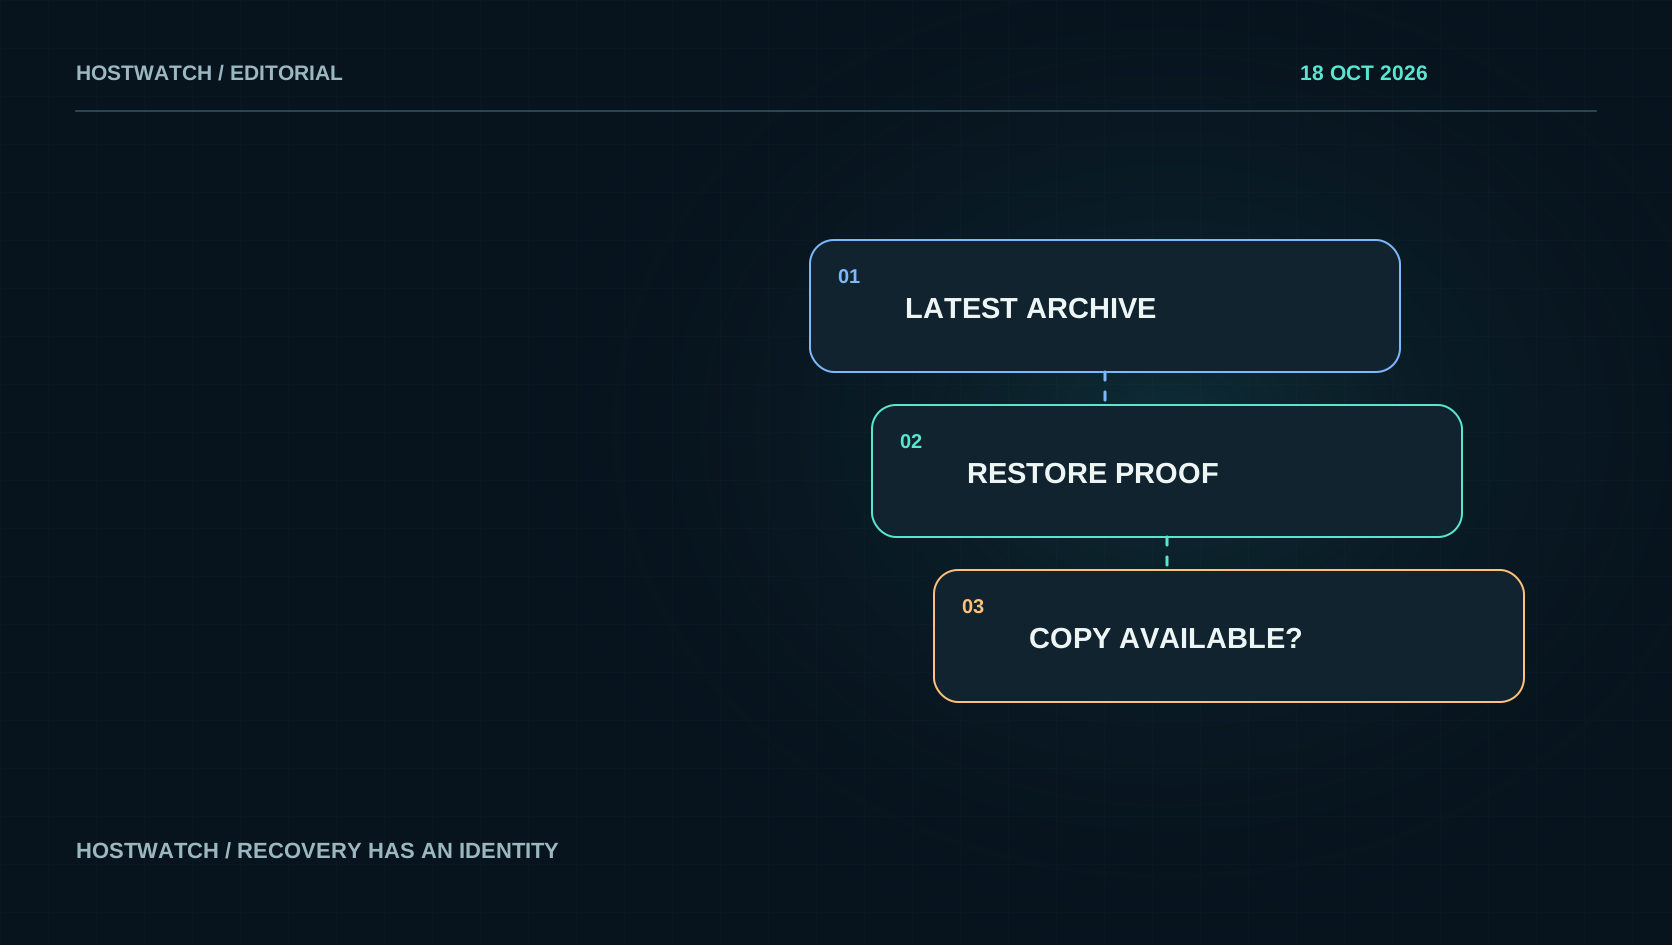
A green backup is not a restore result
A newer archive should not inherit an older restore test. Hostwatch keeps those records separate so an operator can see what exists, what was actually restored and what still needs checking.
Read article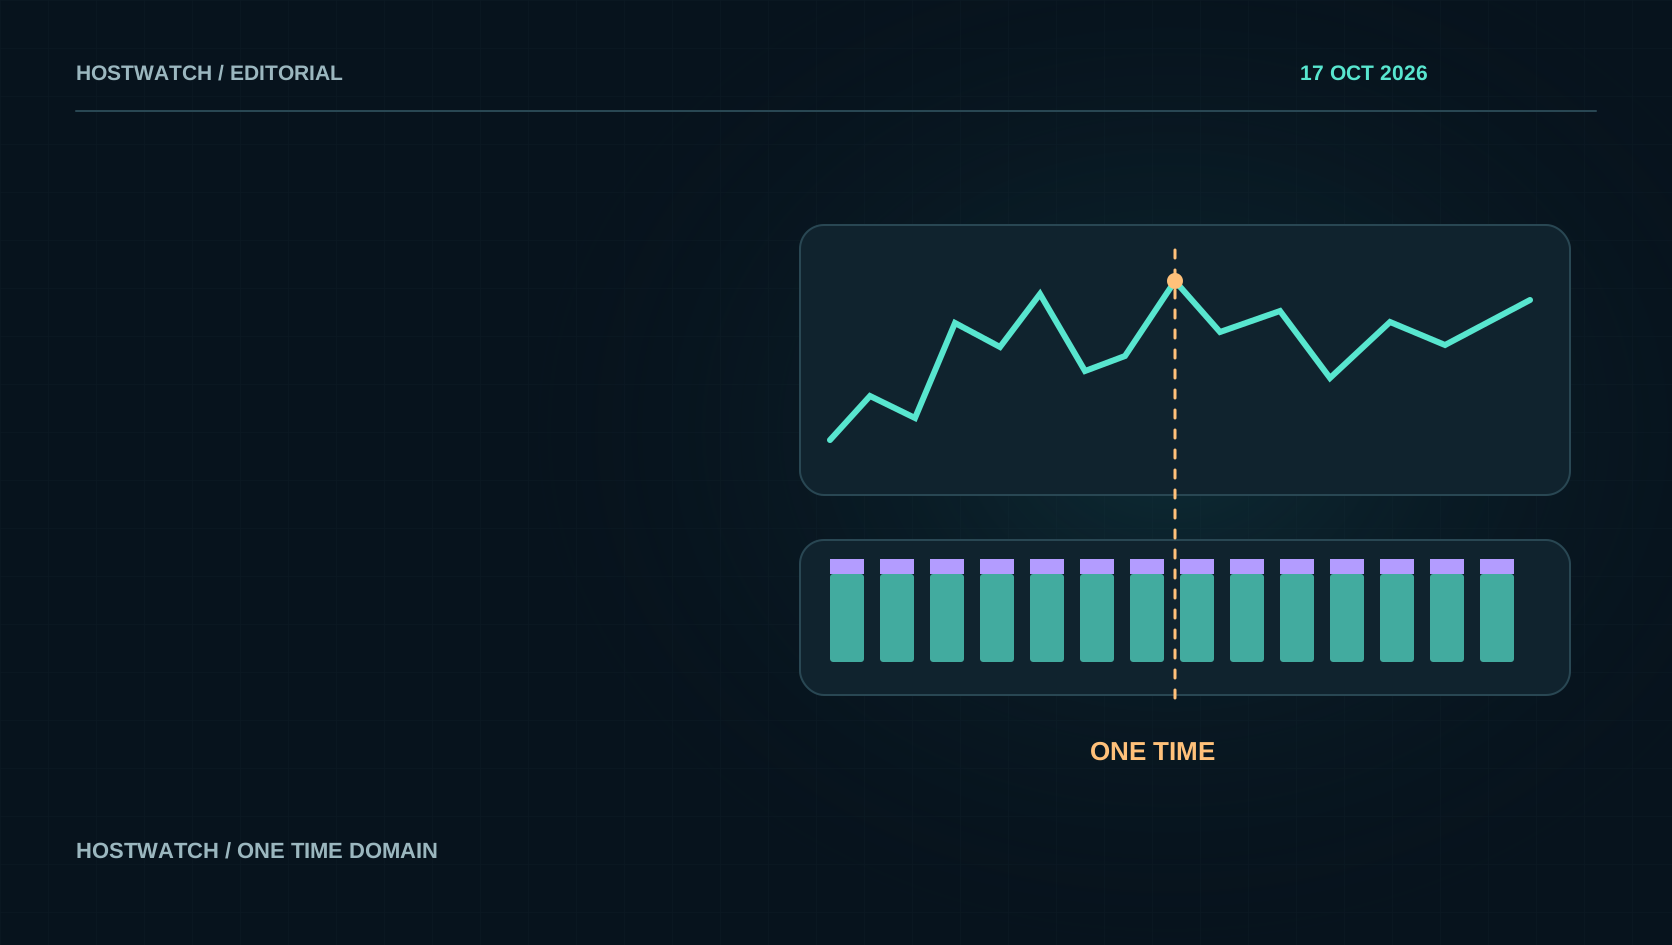
One timestamp, two charts: making resource pressure readable
A CPU line and a workload band should describe the same moment when you drag either chart. That simple expectation requires keeping recorded time, display buckets and evidence coverage separate.
Read article
Hostwatch under HTTP attack load: measuring detection and scoped mitigation
We measured a deliberately small origin before and during a controlled scan, then applied a verified temporary client rule. The test connects a real capacity limit, Hostwatch detection, Nginx enforcement and ordinary-client responses in one reproducible investigation.
Read article
Nginx 429 vs 502 during an HTTP spike: diagnose before you rate limit
A surge can produce both 429 and 502 responses, but they describe different failures. Trace the source of each response before changing a live protection rule.
Read article
Docker and Podman monitoring across servers: build a useful fleet dashboard
A container list is not a fleet dashboard. Connect runtime health, host limits, service identity, logs and safe actions across Docker and Podman servers.
Read article
A million requests, forty examples: building traffic history you can trust
Counters, five-minute summaries and individual requests answer different questions. Here is how to reconcile them before a chart becomes a security decision.
Read article
Connect a private server without surrendering the host
A control plane should learn about a machine only after an owner enrolls an agent and grants a specific capability. Here is a practical model for identity, isolation and revocation.
Read article
Weavatrix Hetero and Hostwatch: private distributed AI across Mac and Linux
A working Mac–Linux model split shows what resource sharing means in practice: an owner controls each contribution, Hostwatch coordinates the workers, and Hetero places the model. These notes examine the integration run recorded on 7 October and reviewed for publication on 10 October.
Read article
Reading an HTTP attack without losing real users
A request spike is a starting point, not a verdict. Connect complete counts, callers, routes and response outcomes before choosing a reversible protection.
Read article
Why detection and mitigation are separate modules
Seeing an anomaly and changing production traffic are different responsibilities. A clear boundary supports observation-only teams, manual response and governed automation.
Read article